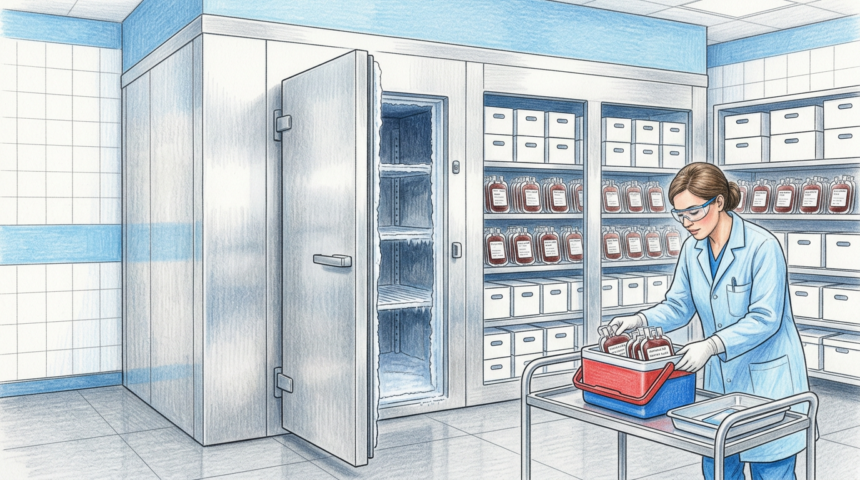
Freezers holding plasma for French hospitals were told to climb from roughly minus 30 degrees Celsius to 110 degrees in the overnight hours of November 1, and the only thing that stopped it was a technician watching a temperature graph.
The French Blood Establishment, known as EFS, confirmed the intrusion on November 2 and said the tampering came through a refrigeration supplier rather than its own network. Thresholds for temperature and defrost cycles on the cold rooms at three sites had been raised to values far outside any safe range. Staff moved the stock to other facilities and brought the affected units under control, so no blood products or samples were lost.
EFS did not name the vendor. French investigative weekly Le Canard enchaine identified the Dutch temperature-control firm Coolworld, which says the incident involved remote monitoring software from another supplier and fell outside its direct control. EFS is working with the national cybersecurity agency ANSSI and the health ministry, and has tightened monitoring on every unit it runs.
For hospitals, the lesson is that environmental controls now sit on the same risk register as the EHR. Cold chain gear, from blood bank compressors to pharmacy refrigerators and tissue banks, is often managed by a third party over a vendor remote-access path that no one on the security team can see. Ask two questions this quarter: which critical storage units can be reached from the internet, and who gets the alert when a setpoint changes at 2am.