MedRisk
  • Home
  • News
    NewsShow More
    Compliance officers review patient files at a workplace health clinic front desk
    A former employee spent months copying files from an employer clinic chain

    Premise Health traced six months of unauthorized record copying to a single…

    November 12, 2026
    Dental practice staff reviewing paper charts at a clinic reception counter
    Small dental practice restored from backup yet still mailed breach notices

    Santa Barbara Endodontics refused to pay an extortion crew and is notifying…

    November 12, 2026
    An unbadged contractor working at a hospital business office desk in bright daylight
    A revenue cycle vendor let a stand-in work under an employee login

    Sutherland Healthcare Solutions ran two years without noticing someone else was performing…

    November 12, 2026
    Hospital security leaders review an incident diagram in a conference room
    CISA wants hospitals to describe how an intruder actually got in

    A revised federal incident form now demands ATT&CK-mapped detail just as a…

    November 12, 2026
    Paramedics redirect an ambulance outside a US hospital emergency department
    A 65-attack tally puts a number on clinical downtime

    Researchers counted the hospital cyberattacks that actually disrupted care and found the…

    November 12, 2026
  • Articles
    ArticlesShow More
    Hand-drawn illustration of a courier carrying a plain parcel up the steps of an apartment building at dusk
    Prescription delivery windows quietly expose behavioral health patients

    Pharmacy courier routes, packaging and doorstep signatures carry more clinical detail than…

    November 4, 2026
    Illustration of nurses carrying paper charts through a hospital ward with monitors switched off
    Downtime drills move up the hospital agenda as attacks keep landing

    Hospital technology leaders are arguing that paper workflows, offline backups and regular…

    October 26, 2026
    Illustration of two executives shaking hands across a boardroom table in a bright office
    Proofpoint moves to absorb Varonis in a $6.3B all-cash deal

    Thoma Bravo's Proofpoint will take Varonis private in the year's largest cybersecurity…

    October 17, 2026
    Alabama mental health authority settles ransomware suit for $700,000
    Alabama mental health authority settles ransomware suit for $700,000

    A 2025 network intrusion that reached more than 30,000 patients ends in…

    October 11, 2026
    Planned Parenthood lab network settles 1.6M patient breach suit
    Planned Parenthood lab network settles 1.6M patient breach suit

    A Seattle clinical laboratory that tests for Planned Parenthood affiliates across 31…

    October 10, 2026
  • Features
    FeaturesShow More
    Few medical devices can make the leap to quantum-safe encryption
    Few medical devices can make the leap to quantum-safe encryption

    A study of 2.5 million connected medical devices found only a sliver…

    October 11, 2026
    Israel's largest HMO pairs its AI rollout with a security vendor
    Israel’s largest HMO pairs its AI rollout with a security vendor

    Israel's largest health maintenance organization is pairing a cybersecurity vendor with its…

    September 30, 2026
    HIPAA security rule overhaul pushed to July 2027 as healthcare sector pushes back

    HHS has delayed the first major HIPAA Security Rule overhaul in over…

    July 12, 2026
    Healthcare Cyberattacks Persist as SonicWall Report Flags Millions of Exploitation Attempts and Rising Ransomware Pressure

    SonicWall’s latest Healthcare Protect Brief warns that healthcare remains the most persistently…

    June 23, 2026
    FTC Warns Tech Giants Against Weakening Encryption or Enabling Censorship

    The agency cautions leading U.S. tech companies that complying with foreign demands…

    May 17, 2026
  • Spotlight
    SpotlightShow More
    Ryuk operator pleads guilty Blackcat AlphV conspirator sentenced to 6 years

    Two ransomware actors face prison time in separate cases involving Ryuk and…

    July 13, 2026
    Legacy Sitecore Flaw Exploited in Healthcare Environments to Deploy WeepSteel Malware

    Mandiant warns that outdated Sitecore configurations in healthcare systems could expose sensitive…

    May 17, 2026
    Three Healthcare Organizations Disclose Major Data Breaches Impacting Over 175,000 Patients

    Recent breaches at CPAP Medical Supplies, a Miracle Ear franchisee, and a…

    May 17, 2026
    Stealthy Prompt Injection in Images Lets Attackers Hijack AI Systems

    Researchers have discovered a method for hiding malicious instructions in images that…

    May 17, 2026
    Transparent Tribe Targets Indian Government With Malicious Desktop Shortcut Files

    The Pakistani-linked APT36 group has expanded its tactics by weaponizing Linux BOSS…

    May 17, 2026
  • About
    • Mission
    • Services
    • Contact
  • Alerts
  • AI Risk
  • Compliance & Legal
  • Cryptography
  • CVEs
  • Data Breaches
  • Malware
  • OT/ICS
  • Phishing
  • Privacy
  • Ransomware
  • Social Engineering
  • Startups
  • Threats
MedRiskMedRisk
Font ResizerAa
  • Home
  • News
  • Articles
  • Features
  • Spotlight
  • Events
Search
  • Quick Links
    • Home
    • News
    • Articles
    • Features
    • Spotlight
  • About MedRisk
    • Mission
    • Services
    • Contact
Have an existing account? Sign In
Follow US
© 2026 MedRisk. All Rights Reserved.
News

A revenue cycle vendor let a stand-in work under an employee login

Sutherland Healthcare Solutions ran two years without noticing someone else was performing an employee's duties on their credentials.

MedRisk Staff
Last updated: November 12, 2026 12:51 am
By
mradmin
Share
2 Min Read
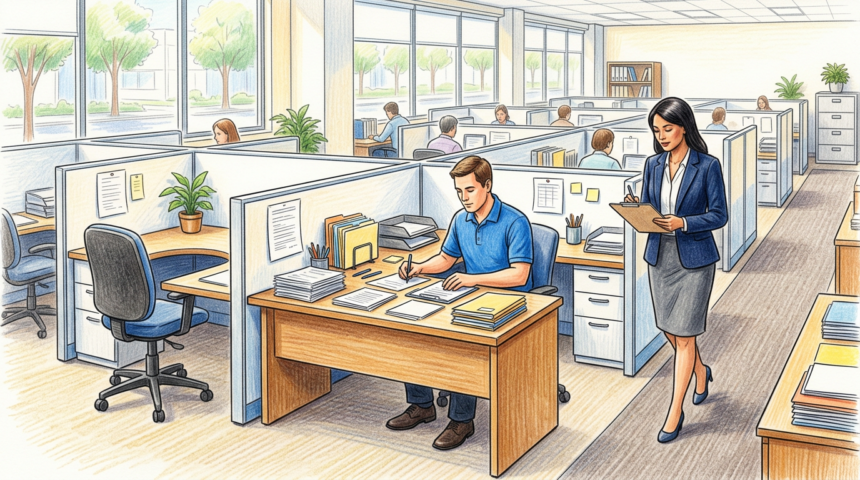
An unbadged contractor working at a hospital business office desk in bright daylight
SHARE

For roughly two years, someone outside Sutherland Healthcare Solutions was doing an employee’s job with that employee’s credentials, and the company did not know.

The revenue cycle and medical coding vendor disclosed that a staff member engaged another individual to perform their duties. That stand-in reached member names, addresses and birth dates, plus health plan and Social Security numbers, claims data and stated gender, from July 29, 2024 through July 10, 2026.

Access died once the arrangement surfaced, and affected health plans were told so they could work out who was exposed. Letters went out recently. Sutherland calls the access non-malicious and reports no misuse, offering identity protection as a precaution. How many people were affected stays undisclosed, and the HHS Office for Civil Rights breach portal carries no entry for it yet.

Hoag finds an intruder the same week

Hoag Memorial Hospital Presbyterian, a nonprofit network in Orange County, California, spotted suspicious network activity on October 8, 2026, and brought in outside forensics. Unauthorized access was confirmed.

By October 25 the review had finished, and Hoag knew that personal and protected health information was involved. Notification letters went out in early November. Publicly filed notices name neither data categories nor an affected population. Credit monitoring has been offered.

The vendor case is the more instructive one. Credential sharing between individuals is nearly invisible to identity controls because the login is valid, no password is stolen, and no malware runs. Contractors and offshore staffing arrangements are the usual setting. Detection depends on correlating behavior – device fingerprint, working hours, location and access pattern – against the account’s history rather than trusting the credential.
TAGGED:Business AssociateCredential SharingData Breachhealthcare vendorHIPAArevenue cycle
SOURCES:The HIPAA Journal
Share This Article
Email Copy Link Print
Previous Article Hospital security leaders review an incident diagram in a conference room CISA wants hospitals to describe how an intruder actually got in
Next Article Dental practice staff reviewing paper charts at a clinic reception counter Small dental practice restored from backup yet still mailed breach notices

You May also Like

Hand-drawn illustration of a senior patient looking at a blank smartphone with a family member nearby
News

MyChart phishing wave dangles free Medicare kits at patients

August 24, 2026
Hospital security team reviewing ransomware defenses in a bright conference room
News

SafePay hits 600 victims as agencies flag its edge device playbook

October 25, 2026
Medical files of FBI staff surface in a ShinyHunters extortion haul
News

Medical files of FBI staff surface in a ShinyHunters extortion haul

September 28, 2026
ArticlesNews

Healthcare data breach settlements mount with ransomware and pixel tracking payouts

July 12, 2026
Show More
MedRisk

The latest in healthcare & medical technology risk
From breaking news to expert analysis, our coverage helps professionals stay informed, secure, and ahead of the threat curve.

X-twitter Youtube Linkedin

© 2026 MedRisk. All rights reserved. Privacy | Legal

Quick Links

  • News
  • Articles
  • Features
  • Spotlight
  • Events
  • Mission
  • Services
  • Contact
Welcome to Foxiz
Username or Email Address
Password

Lost your password?